The answers your security review needs.
Governance is not a page in the trust center. It is whether the platform can enforce a rule you wrote. Infrastructure for AI needs guardrails, and Ward is the warden that enforces them: policy evaluated at query time, for every caller, including the ones that are not people.
Row- and column-level policies applied in real time, per-tenant isolation, and one access log for people and agents.
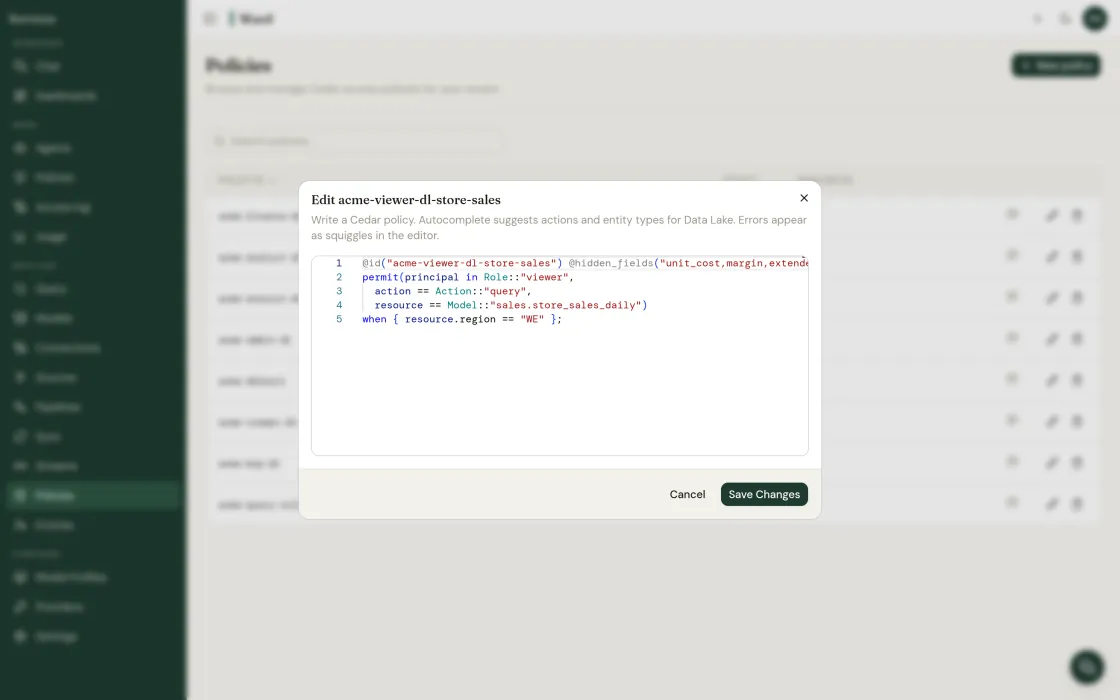
Row- and column-level Cedar policies, applied in real time on every query, not in the client.
Ward AI drafts access policies from plain English. Nothing binds until a human approves it.
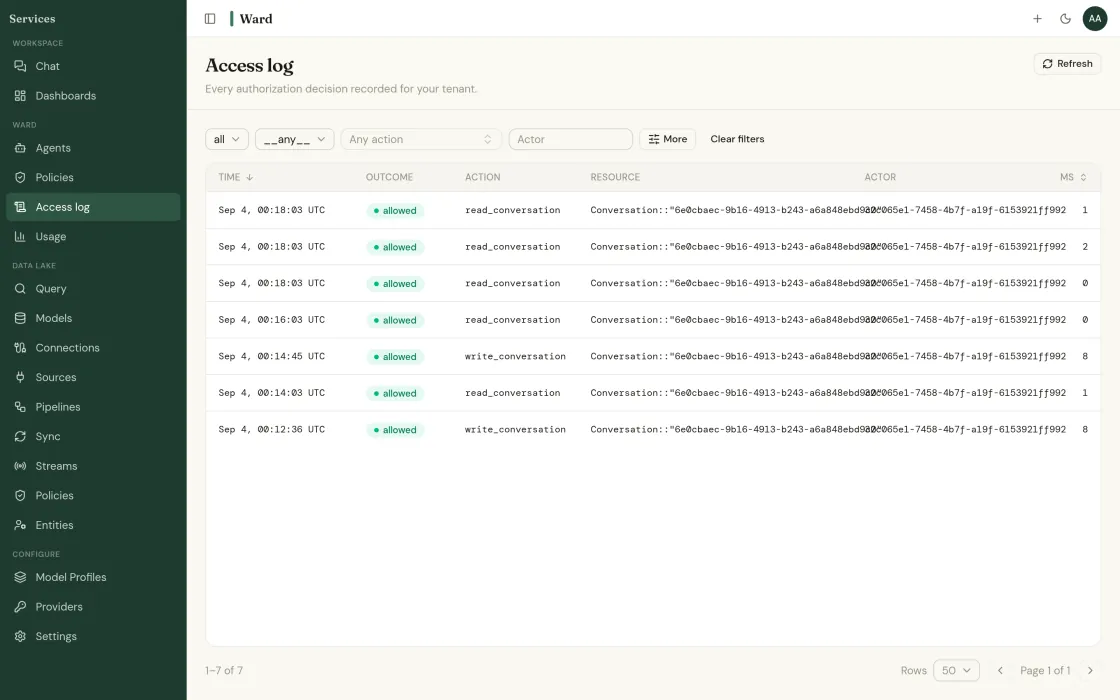
Every access logged with the policy that allowed or denied it, for people and agents alike.
Customer data physically isolated per tenant. Only schemas and settings are gated in the application.
SSO through OpenID Connect. Your cloud, ours, or on-prem, including air-gapped.
Policy as code.
Not click-admin drift.
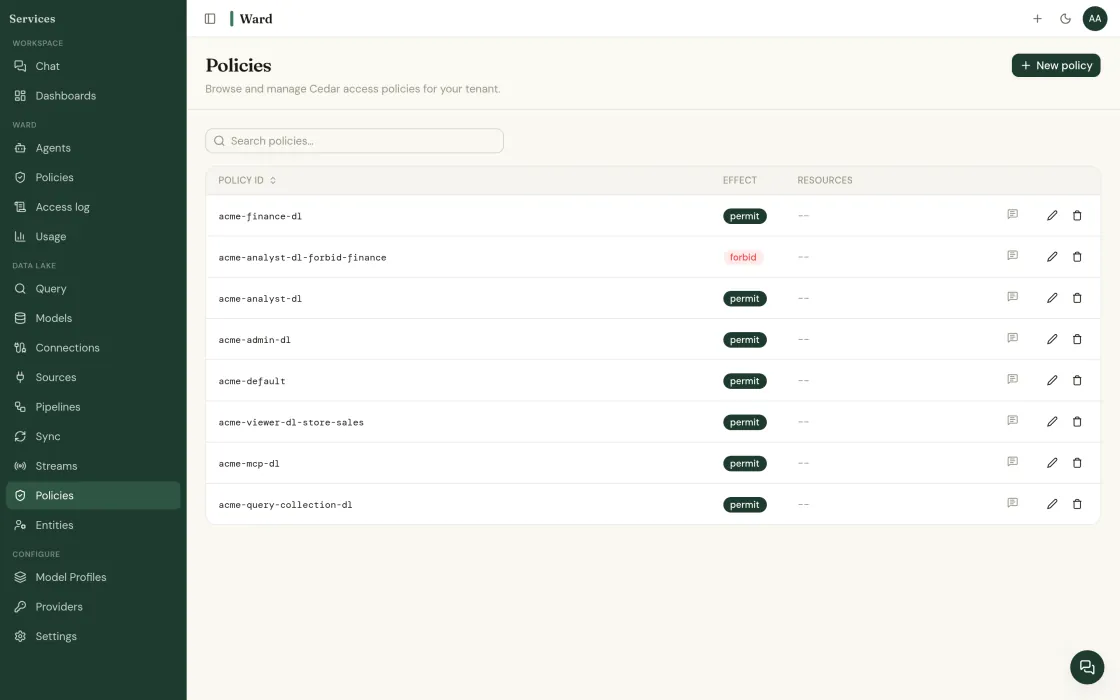
The policy plane, kill switch and audit trail your team would otherwise build with a free quarter. Policies are Cedar, written and versioned inside your tenant, and every decision made under them is recorded.
-
Ward AI drafts. You approve.Ward AI drafts the Cedar policy from a plain-English brief and nothing binds until you save it. The editor autocompletes actions and entity types against your own models and underlines errors as you type.
-
Scoped per role, tenant, resourceFinance Agent cannot see labor schedules. Vendor Agent cannot touch shrinkage. US tenant cannot query EU tables. Least-privilege, machine-enforced.
-
Classifications drive accessTag a column
pii,financial, oroperationalonce. Every agent and query inherits the rule. -
Who changed what, on the recordCharter edits, prompt changes, policy updates: logged with name, time, ticket, approver. Diff, roll back, export to your SIEM.
-
Writes need a named humanExports, write-backs, schedule pushes. Anything that mutates state gates on a role you define, logged with the approver.
-
Audit any number on the pageClick a forecast, a margin call, a shrink flag. Ward shows the query, source rows, model, parameters, and backtest.
What this looks like when you actually use it.
Least privilege by default
Read-only credentials, scoped to named schemas. Write access is granted per table and per action. There is no mode in which Ward holds an admin role on your warehouse.
Policy at query time
Row- and column-level Cedar policies are applied when the query runs, for every caller, and each access is logged with the policy that allowed or denied it. A rule enforced in the client is not enforced at all. Agents run with the permissions of the person who starts them.
Five more primitives. Adopt them in any order.
Data lake
Its own engine. Query in place or sync.
Ward's own data lake engine: columnar, indexed, partitioned and clustered, with live databases joined in place.
Read more →Connectors
540 sources. Read-only by default.
Managed ingestion from warehouses, lakes, SaaS APIs, databases and flat files.
Read more →Semantic layer
One definition of revenue. Enforced.
Metrics, dimensions and grain defined once and enforced everywhere, including in what agents are allowed to compute.
Read more →Agent runtime
The warden of your data and your agents.
Agents on your own data that run with the permissions of the person who starts them, with every access logged.
Read more →Query and chat
Ask in English. Every answer shows its work.
Natural language across every source, with each figure linked to its query and source rows.
Read more →Start with one source.
Deploying is free. The whole console, every connector, and nothing to license.
Read-only to start · your LLM keys · SOC 2 Type II underway · or book a call directly
Find out what your data has been hiding.
Tell us about your operation. We’ll show you the problems Ward catches, and the ones your current tools miss.